You’ve probably heard that Bitcoin is "immutable." It’s a word thrown around in crypto Twitter and boardrooms alike, implying that once a transaction lands on the chain, it’s carved in digital stone forever. But here’s the tricky part: SHA-256, the cryptographic hash function at the heart of Bitcoin, doesn’t actually make transactions immutable by itself. If you change one character in a transaction’s data, SHA-256 spits out a completely different output, sure. But does that mean an attacker can’t just rewrite history? Not exactly.
The real magic isn’t in the hash alone-it’s in how Bitcoin combines SHA-256 with digital signatures, Merkle trees, and economic incentives to make tampering not just difficult, but prohibitively expensive. Think of SHA-256 as the lock, but the entire blockchain architecture is the vault, the guard dogs, and the alarm system combined. If you’re trying to understand why your Bitcoin transfer won’t suddenly vanish or get altered by a hacker, you need to look beyond the hash function and see the whole picture.
What Is SHA-256 and Why Does Bitcoin Use It?
SHA-256 is a member of the Secure Hash Algorithm 2 family, designed by the U.S. National Security Agency and standardized by NIST in 2001. It takes any input-whether it’s a single letter or the entire text of *War and Peace*-and crunches it into a fixed-size 256-bit (32-byte) string called a digest. The key property here is determinism and avalanche effect: tiny changes in the input result in wildly different outputs.
Bitcoin doesn’t use SHA-256 once; it uses it twice. This is known as Double SHA-256 or SHA-256d. When you send Bitcoin, the network creates a unique identifier for your transaction, called a txid, by hashing the serialized transaction data twice. This txid acts like a fingerprint. If someone tries to tweak the amount you sent or the recipient’s address, the txid changes instantly. Nodes across the network check this fingerprint against their copy of the ledger. If it doesn’t match, they reject the transaction.
| Property | Description | Security Strength |
|---|---|---|
| Output Size | Fixed 256-bit digest regardless of input size | N/A |
| Preimage Resistance | Hard to find an input that produces a specific hash | 256 bits |
| Collision Resistance | Hard to find two inputs that produce the same hash | 128 bits (generic attack) |
| Avalanche Effect | Small input change causes massive output change | High sensitivity |
The Merkle Tree: Committing to Every Transaction
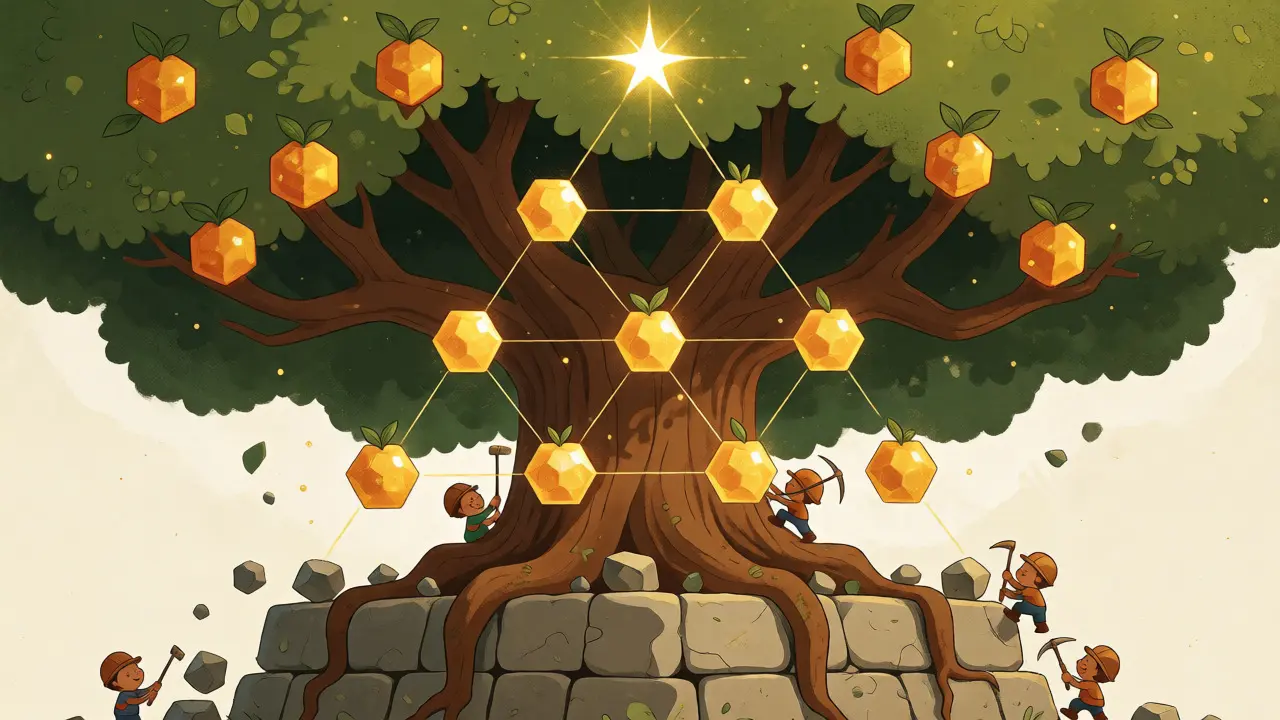
If SHA-256 fingerprints individual transactions, the Merkle Tree is the structure that bundles all those fingerprints into a single commitment for each block. Imagine a tournament bracket where every transaction plays against another. Their hashes are paired and hashed together again. Winners advance, get hashed again, until only one hash remains at the top. This is the Merkle Root.
This root goes into the block header. Here’s why that matters for tamper resistance: if an attacker wants to change a transaction deep inside a block, they have to recalculate its txid. That change ripples up through the tree, altering the Merkle Root. Since the Merkle Root is part of the block header, changing it invalidates the block’s proof-of-work. You can’t just swap a transaction in a past block without breaking the entire chain’s mathematical consistency.
It also allows for efficient verification. A light client (like a mobile wallet) doesn’t need to download every transaction in a block to prove yours was included. It just needs a short path of hashes-a Merkle Proof-to show your transaction connects to the valid Merkle Root.
Proof-of-Work: The Economic Moat
Hashing detects changes, but Proof-of-Work makes rewriting history expensive. Miners compete to find a nonce (a random number) that, when hashed with the block header, produces a result below a certain target difficulty. This requires brute-force guessing billions of times per second.
Each block contains the hash of the previous block. This creates a chain. If you want to alter a confirmed transaction in Block #800,000, you must:
- Recalculate the Merkle Root for Block #800,000.
- Find a new valid nonce for Block #800,000.
- Recompute the proof-of-work for every subsequent block (Block #800,001, #800,002, etc.).
- Do all this faster than the rest of the network adds new blocks.
This is where economics kicks in. To overtake the honest chain, an attacker needs more computational power than the rest of the network combined. As of late 2025, estimates suggest acquiring enough ASIC hardware to achieve a 51% hash rate could cost upwards of $11 billion before electricity costs even enter the equation. It’s not impossible, but it’s financially ruinous for most actors.
Immutability Is Probabilistic, Not Absolute
People often say Bitcoin is "unhackable." That’s misleading. Bitcoin is computationally secure. There is no law of physics preventing a change; there is just a mountain of work required to make it stick.
Consider confirmations. A transaction in the mempool (waiting area) has zero confirmations and can be replaced. Once included in a block, it has one confirmation. Each additional block built on top adds more work protecting that history. The probability of an attacker catching up decreases exponentially with each confirmation. For small coffee purchases, one confirmation might suffice. For moving millions in dollars, exchanges often wait for six confirmations.
Even with high confirmations, risks remain. A 51% Attack allows an attacker to reorganize recent blocks, potentially double-spending their own coins. However, they cannot steal coins from others because they don’t have the private keys. They also can’t create new coins outside the protocol rules. SHA-256 protects integrity; consensus rules protect validity.
Real-World Limitations and Risks
SHA-256 is robust, but it’s not a silver bullet. The biggest threats to Bitcoin transactions aren’t usually hash collisions-they’re human and operational errors.
- Private Key Theft: If malware steals your keys, you lose your funds. No amount of hashing saves you from signing a bad transaction.
- Transaction Malleability: Historically, some non-functional changes to signature data could alter a txid without changing the transaction’s meaning. Segregated Witness (SegWit), activated in 2017, largely solved this by separating signature data from the txid calculation.
- Software Bugs: Flaws in wallet software or node implementations can lead to lost funds or rejected transactions.
- Exchange Compromise: Centralized exchanges hold your keys. If they get hacked, your on-chain immutability doesn’t help if the off-chain ledger is manipulated.
Also, remember that SHA-256 is a one-way function. It hides nothing. Anyone can look at a transaction and see the amounts and addresses. It proves integrity, not privacy.
How to Verify Your Own Transactions
You don’t need to trust a centralized authority to verify your Bitcoin. You can run a full node. This involves downloading the entire blockchain history and validating every rule independently. If you’re a developer, you can test this logic yourself:
- Take a simple message like "Hello Bitcoin".
- Run it through SHA-256 twice.
- Note the output.
- Change one letter to "hello bitcoin".
- Hash it again.
- See the complete difference in output.
This demonstrates the avalanche effect. In a production environment, your node does this for every transaction in every block, ensuring no unauthorized alterations slipped through.
Frequently Asked Questions
Can quantum computers break SHA-256 in Bitcoin?
Quantum computers pose a theoretical threat via Grover's algorithm, which could halve the effective security strength of SHA-256 from 256 bits to 128 bits. While 128 bits is still considered strong against current technology, it reduces the margin of safety. However, Bitcoin’s ECDSA signatures are more vulnerable than SHA-256. Most experts believe Bitcoin will migrate to post-quantum cryptography long before quantum computers become powerful enough to threaten SHA-256 significantly.
Does SHA-256 encrypt my Bitcoin transaction?
No. SHA-256 is a hash function, not encryption. Encryption is reversible with a key; hashing is a one-way process. Your transaction details (sender, receiver, amount) are visible to everyone on the network. SHA-256 ensures that these details haven't been changed, but it doesn't hide them.
What happens if I change a transaction after it's confirmed?
If you try to submit a modified version of a confirmed transaction, nodes will reject it because its txid won't match the one recorded in the blockchain. To successfully alter a confirmed transaction, an attacker would need to rewrite the entire chain from that point forward, requiring immense computational power to overtake the honest network.
Why does Bitcoin use double hashing (SHA-256d)?
Double hashing provides defense-in-depth against potential vulnerabilities in single-pass hashing algorithms. It mitigates length-extension attacks, which are possible in some Merkle-Damgård constructions like standard SHA-256. By hashing the output again, Bitcoin ensures that partial information about the internal state isn't leaked, enhancing overall security.
Is Bitcoin truly immutable?
Bitcoin is probabilistically immutable. Recent blocks can be reorganized during forks. Older blocks are increasingly secure due to accumulated proof-of-work. While theoretically possible to rewrite history, the economic cost makes it impractical for anyone other than a nation-state or cartel with massive resources, and even then, only for recent transactions.