You hold governance tokens on Ethereum, but the protocol you want to vote on lives on Arbitrum. Or maybe your treasury is split across five different networks, and every time a proposal passes, someone has to manually bridge funds or execute transactions on each chain separately. This fragmentation is the silent killer of decentralized autonomy. If your DAO requires users to bridge assets just to cast a vote, or if passing a proposal means coordinating six separate smart contract calls, you aren't truly autonomous-you're bottlenecked by interoperability.
Multi-chain governance is the architectural approach that allows a single governance process to recognize voting power, collect votes, reach a decision, and execute instructions across two or more independent blockchain networks. As of late 2026, there is no single universal standard for this. Instead, we have several competing architectures, each with distinct trade-offs in security, speed, and complexity. The goal isn't just convenience; it's about unified control over treasuries and deployments without forcing every voter to become a bridge expert.
The Core Problem: Fragmented Truth
On a single chain, truth is simple. A token holder’s balance, their vote, and the resulting execution all happen within one state machine. When you go multi-chain, that state machine breaks into pieces. Your voting power might be on Chain A, while the action needs to happen on Chain B. A robust system must solve four specific problems simultaneously:
- Source of Truth: Where does the official vote tally live?
- Transport: How do you move authenticated messages or proofs between chains?
- Prevention: How do you stop a user from voting twice using the same tokens (double-spending governance)?
- Execution: How do you safely trigger actions on the destination chain without risking replay attacks or stale data?
If any of these fail, your DAO can end up executing conflicting proposals or losing funds to bridge hacks. In fact, a 2026 empirical analysis of bridge attacks reported gross losses of $2.676 billion between 2022 and 2026, with proof forgery and credential seizure accounting for over 86% of those losses. This context matters: treating cross-chain governance as "just another API call" is a dangerous mistake.
Architecture 1: Hub-and-Spoke (Wormhole MultiGov)
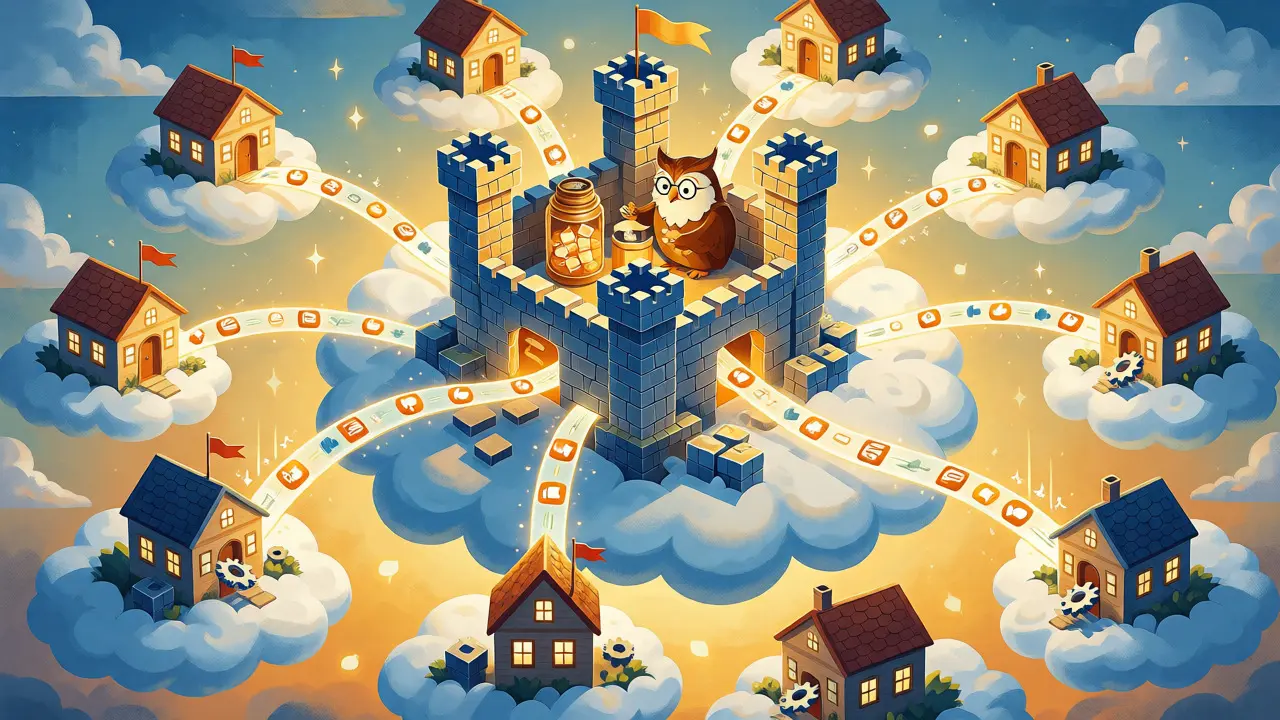
The most explicit production-ready model today is the hub-and-spoke design, exemplified by Wormhole MultiGov. In this setup, one chain acts as the "hub"-typically Ethereum Mainnet due to its high security-and other chains are "spokes." The hub stores the canonical governance state, handles proposal creation, and aggregates votes. Spoke chains allow local token holders to participate, but they don't make final decisions independently.
Here is how the flow works in practice:
- A proposal is created on the hub chain.
- Voters on spoke chains cast votes using a
SpokeVoteAggregator. - These votes are transmitted via Wormhole messaging to the hub’s
HubVotePool. - The hub tallies the votes. If quorum is met, the proposal executes locally after a timelock.
- A
HubMessageDispatchersends instructions to spoke chains, where aSpokeMessageExecutorverifies and runs them.
This architecture shines because it keeps the source of truth singular. However, it introduces dependencies. If the hub chain experiences congestion, or if the message relay fails, execution stalls. It also requires strict technical prerequisites: the governance token must implement OpenZeppelin-style ERC20Votes, and the system relies on timestamp-based snapshots rather than block numbers, since block heights aren't comparable across heterogeneous chains.
Architecture 2: Storage Proofs (Snapshot X)
If you prefer not to trust a message relay, you might look at Snapshot X. Unlike traditional off-chain Snapshot, which relies on signed messages, Snapshot X is an on-chain protocol deployed on EVM chains and Starknet. Its standout feature for multi-chain governance is the use of storage proofs.
Instead of sending a message saying "User X voted," the system proves that User X had voting power at a specific point in time on another chain. For example, on Starknet, the protocol can verify the state of an Ethereum contract at a specific block hash. This avoids trusting a conventional bridge for the specific fact of voting power. You aren't relying on a relayer to tell you what happened; you're mathematically verifying the history.
The trade-off? Complexity. Generating these proofs requires specialized infrastructure and compatible state layouts. It offers stronger censorship resistance and verifiability than off-chain systems, but it imposes higher deployment costs and integration hurdles. It’s ideal for DAOs that prioritize cryptographic certainty over ease of implementation.
Architecture 3: General Message Passing (LayerZero)
Some DAOs don't want a pre-built governance product; they want to build their own logic. LayerZero provides the plumbing for this via its OApp (Omnichain Application) standard. It doesn't give you a governance module out of the box. Instead, it lets developers send arbitrary data between smart contracts on multiple chains.
With LayerZero, your DAO defines the rules. You decide how to encode the proposal, how to handle quorums, and what constitutes valid execution. The network uses configurable verifier networks called DVNs (Decentralized Verifier Networks). You choose the security level: do you want three independent verifiers? Five? Each configuration changes the cost and the trust assumptions.
| Feature | Wormhole MultiGov | Snapshot X | LayerZero OApp | Cosmos ICS-27 |
|---|---|---|---|---|
| Model | Hub-and-Spoke | Storage Proofs | General Messaging | Native Interchain Accounts |
| Trust Assumption | Relayer/Guardian Network | Cryptographic Proof | Configurable DVNs | IBC Light Clients |
| Complexity | Moderate | High | High (Custom Logic) | Low (Within Cosmos) |
| Best For | EVM-heavy DAOs needing quick setup | DAOs prioritizing verification over speed | Teams building custom governance logic | Cosmos SDK ecosystems |
The advantage here is flexibility. You can tailor the governance experience exactly to your community's needs. The disadvantage is responsibility. LayerZero explicitly recommends protecting critical owner roles with multisigs or timelocks. If you misconfigure your DVN settings or forget to verify ownership after a chain rollout, you open yourself to exploits. There is no universal price list; costs vary by message size and chosen security parameters.
Architecture 4: Native Interoperability (Cosmos ICS-27)
Outside the EVM world, the Cosmos ecosystem solves this differently. Interchain Accounts (ICS-27) allow a controller chain to control an account on a host chain through IBC packets. Think of it as having a bank account on Bank B that you manage entirely from Bank A.
In a DAO context, the governance module on the controller chain approves a transaction, and the interchain account executes it on the host chain. This is seamless for Cosmos SDK chains but doesn't automatically translate to unrelated networks like Ethereum or Solana. You still need to define quorum models and handle timeouts, but the underlying transport layer is native to the ecosystem, reducing reliance on external bridges.
Security Pitfalls and Best Practices
No matter which architecture you choose, security is non-negotiable. A cross-chain vote can fail through forged proofs, compromised signers, or replayed messages. Here is a checklist for hardening your system:
- Canonical Identifiers: Define unique proposal IDs, chain IDs, and nonces. Never rely on timestamps alone for ordering.
- Replay Protection: Ensure a message can only be executed once per destination chain.
- Finality Bounds: Wait for sufficient confirmations on the source chain before sending a message. Don't act on pending states.
- Idempotent Execution: Design destination contracts so that re-running the same instruction doesn't cause errors or double-spend funds.
- Timelocks: Always include a delay between vote passage and execution. This gives users time to exit if they disagree with the outcome.
Uniswap’s approach highlights another layer: multi-message aggregation. By having multiple bridge providers relay the same message and using a multisig to select the correct payload, you reduce dependence on a single provider. It’s heavier on coordination but safer against single points of failure.
Which Path Should You Take?
Choosing the right system depends on your DAO's maturity and risk tolerance.
If you are launching quickly and operate primarily on EVM chains, Wormhole MultiGov offers the fastest path to production. It handles the heavy lifting of aggregation and dispatching. If you are a highly technical team with unique governance requirements, LayerZero gives you the raw materials to build exactly what you want, provided you have the resources for rigorous auditing.
For communities that value absolute transparency and are willing to pay for computational overhead, Snapshot X’s storage-proof model is compelling. And if you are already deep in the Cosmos ecosystem, ICS-27 is the natural, low-friction choice.
Remember, cross-chain governance cannot be more secure than its weakest link. Whether that link is a bridge, a relayer, or your own smart contract code, assume it will be attacked. Test for malformed messages, delayed deliveries, and partial failures. The goal isn't just to connect chains-it's to keep your DAO autonomous even when the connections get messy.
Do voters need to bridge their tokens to vote?
No, not necessarily. In systems like Wormhole MultiGov, voters can often vote from their local chain using their local balance, which is then aggregated on the hub chain. However, some architectures may require bridging for specific execution steps or if the voting power calculation relies on direct access to the token contract on the destination chain.
What happens if a cross-chain message fails to deliver?
Most robust systems include retry mechanisms or manual execution triggers. If a message fails, the proposal usually remains in a 'pending' state until the message is successfully delivered or manually triggered by an authorized actor. Timelocks often provide a buffer window for these retries.
Is cross-chain governance slower than single-chain governance?
Yes, typically. It involves waiting for source chain finality, message transmission time, and destination chain execution. This adds latency compared to immediate on-chain execution. However, modern protocols like LayerZero and Wormhole have significantly reduced this gap, making delays measured in minutes rather than hours.
Can a hacker exploit a cross-chain vote?
Absolutely. Attack vectors include forging proofs, compromising relayers, or exploiting race conditions during message delivery. Historical data shows billions in losses from bridge-related incidents, so rigorous auditing and formal verification of the governance contracts are essential.
Which architecture is best for new DAOs?
For most new EVM-based DAOs, a hub-and-spoke model like Wormhole MultiGov is often the pragmatic choice due to its established tooling and documentation. It balances ease of integration with sufficient security for early-stage projects.